Inspect a JWT payload: a fictional example without signature verification
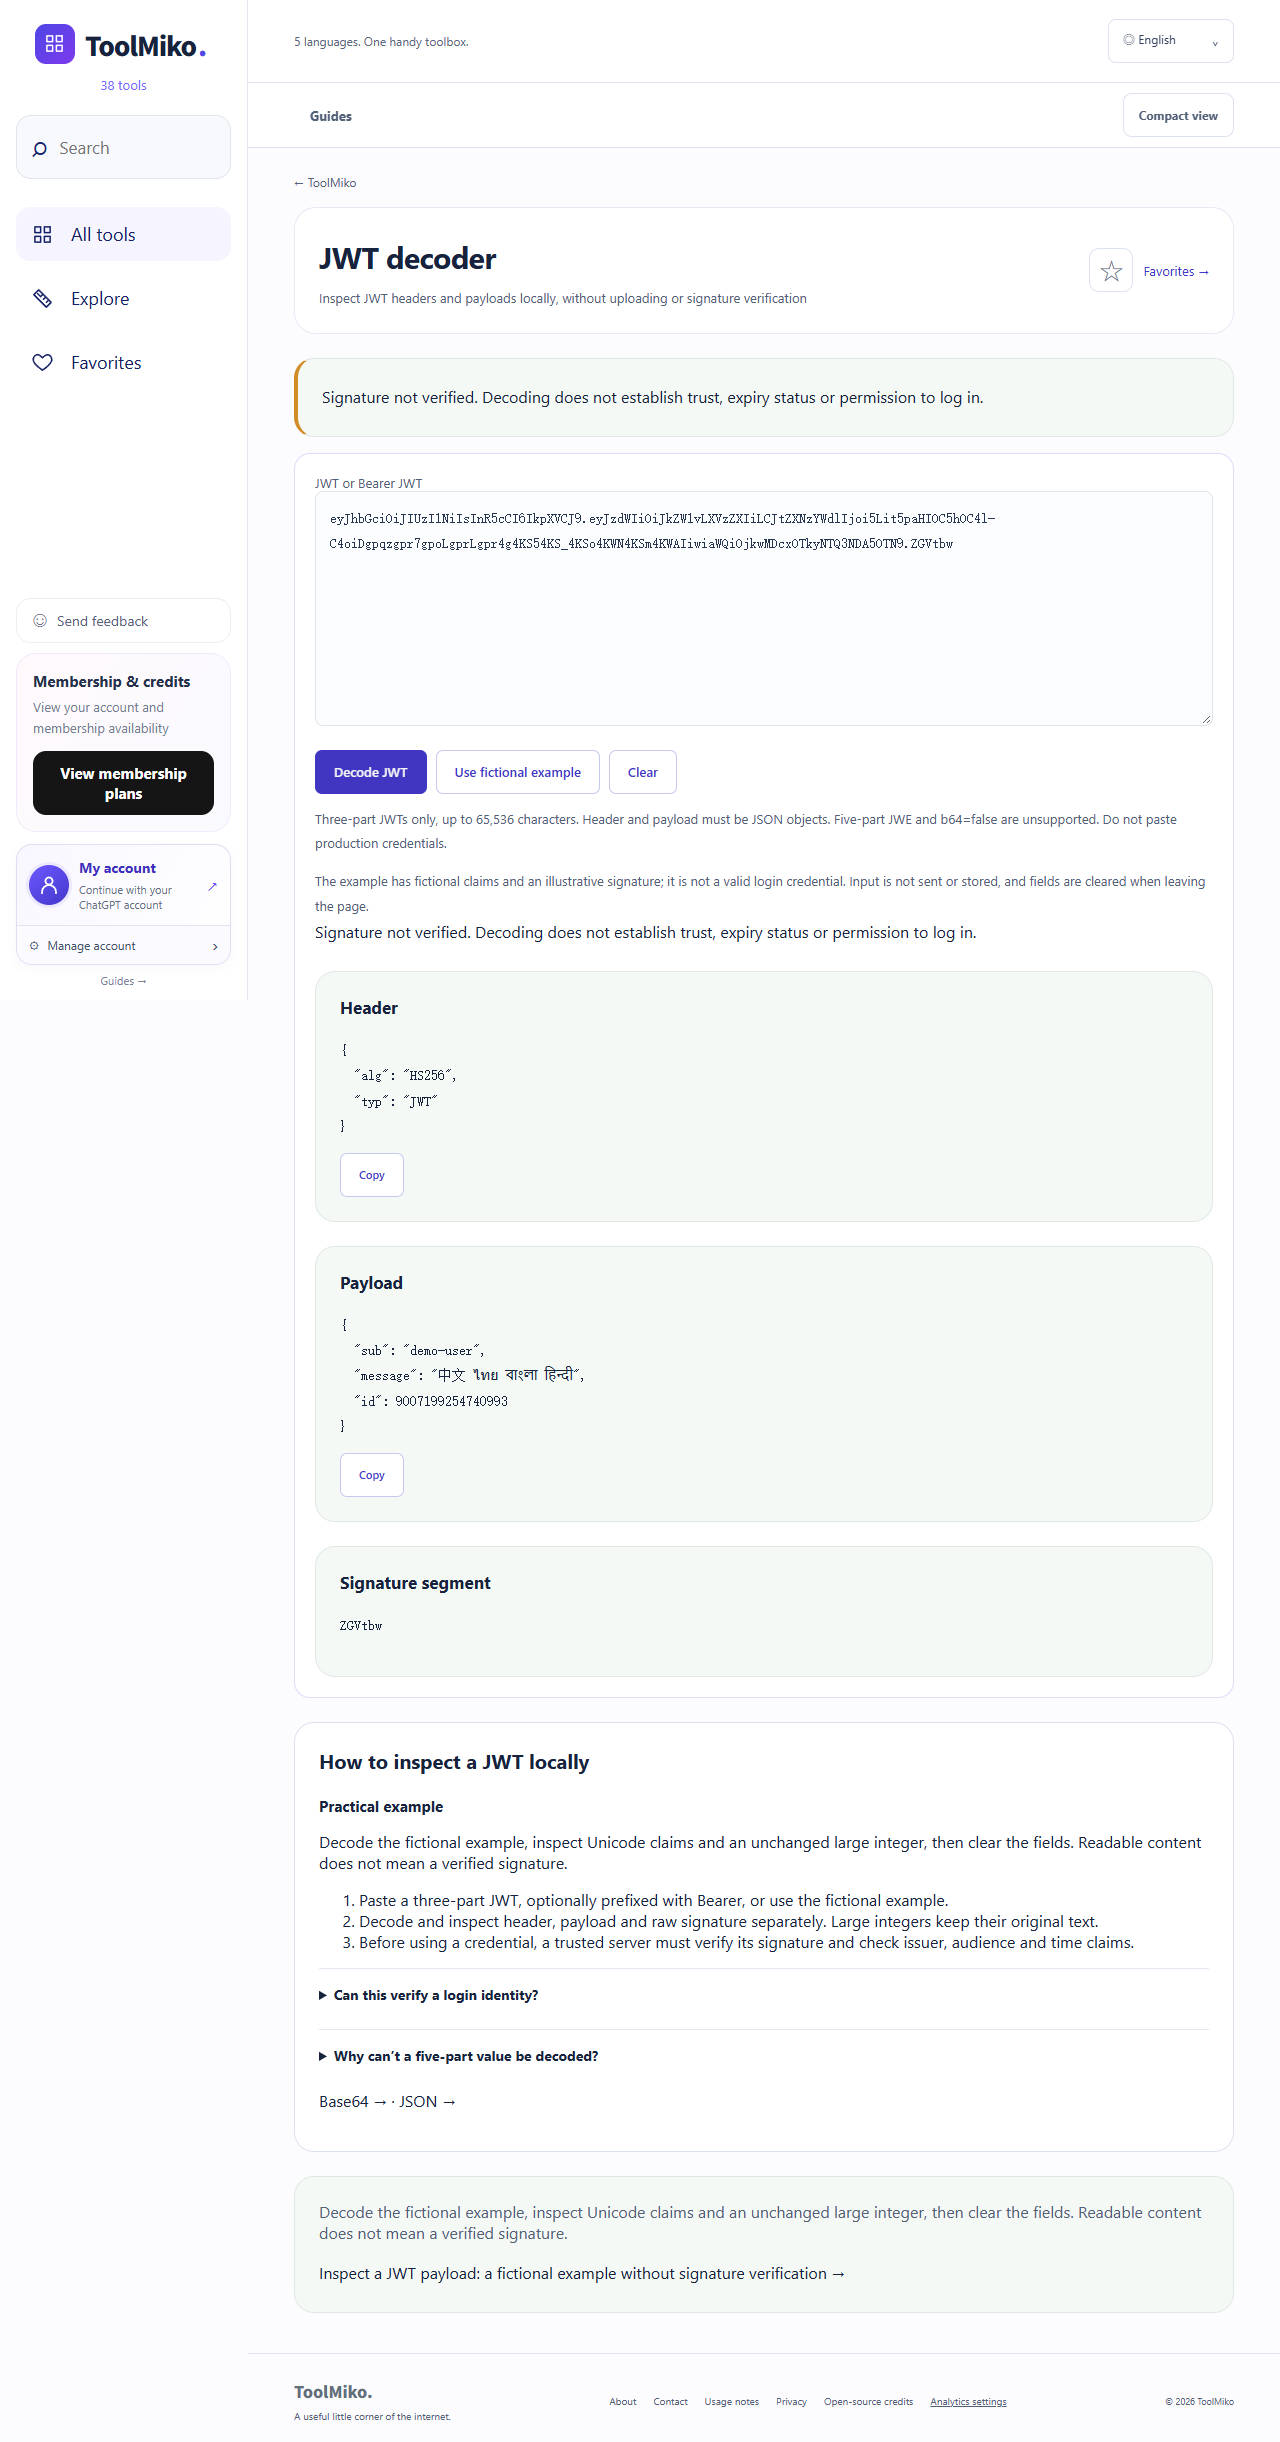
Decode the fictional example, inspect Unicode claims and an unchanged large integer, then clear the fields. Readable content does not mean a verified signature.
Open tool: JWT decoder →What should you prepare?
- The example has fictional claims and an illustrative signature; it is not a valid login credential. Input is not sent or stored, and fields are cleared when leaving the page.
- Three-part JWTs only, up to 65,536 characters. Header and payload must be JSON objects. Five-part JWE and b64=false are unsupported. Do not paste production credentials.
How do you use ToolMiko?
- Paste a three-part JWT, optionally prefixed with Bearer, or use the fictional example.
- Decode and inspect header, payload and raw signature separately. Large integers keep their original text.
- Before using a credential, a trusted server must verify its signature and check issuer, audience and time claims.
What did the sample produce?
Decode the fictional example, inspect Unicode claims and an unchanged large integer, then clear the fields. Readable content does not mean a verified signature. Signature not verified. Decoding does not establish trust, expiry status or permission to log in.
| Check | Observed result |
|---|---|
| Input | Fictional three-part JWT; not a valid credential |
| Observed result | unicode=preserved; integer=9007199254740993; signature_verification=not_performed; private_input_storage=none |
| File bytes | 233 |
These non-personal samples were generated for ToolMiko and tested in Windows Chrome on 2026-11-13. Repeat with the source files; results can differ with your files and device.
What if the result is wrong?
Can this verify a login identity?
No. It only decodes. It does not validate signatures, keys, trusted algorithms, expiry or permissions. Never grant access based on the decoded output.
Why can’t a five-part value be decoded?
This tool accepts three-part text JWTs. Encrypted JWE, non-JSON payloads and unencoded payloads are outside its scope.
Limits and file handling
Three-part JWTs only, up to 65,536 characters. Header and payload must be JSON objects. Five-part JWE and b64=false are unsupported. Do not paste production credentials. Signature not verified. Decoding does not establish trust, expiry status or permission to log in.